

Open Finance risk: Nine things that happened in September you need to know about
Louise Beaumont | Insights, Women In Open Banking
01 Oct 2026
September brought a UK payments scheme going live, new US federal guidance on third-party risk, and six global banks agreeing on AI agent liability – none of it coordinated, all pointing at the same gap.
The UK’s Open Banking ecosystem is about to get a lot bigger, a lot faster
Ozone API can now take any non-CMA9 UK bank live on commercial Variable Recurring Payments (cVRP) in eight to 10 weeks, and the UK Payments Initiative (UKPI) gives them a scheme to plug into. Every account information service provider (AISP) and payment initiation service provider (PISP) clears a regulatory bar to operate. What is missing is monitoring after that point, and shared visibility when one bank spots a problem. More here.
Andrew Bailey’s AI warning to the G20 is really a warning about concentration
Bank of England governor Andrew Bailey warned the G20, as chair of the Financial Stability Board (FSB), that frontier AI is the most immediate cyber risk to the global financial system, driven by concentrated third-party providers. The UK oversees four Critical Third Parties for cloud infrastructure, but not the frontier AI model providers Bailey’s letter is about – a gap forming one layer beneath Open Finance too. More here.
The FCA’s mortgage sprint solved for trusted data, not trusted entities
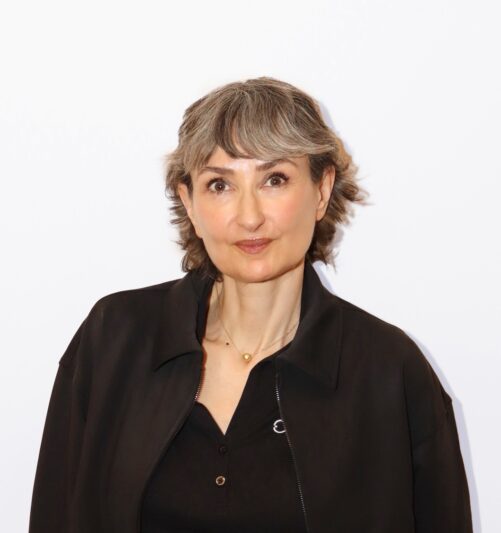
Louise Beaumont, head of marketing and communications at Invela
The Financial Conduct Authority’s (FCA’s) mortgage sprint report coined the term “decision-grade data”: accurate, current, standardised, verifiable. But every mechanism it proposes trusts the data, not the entity holding it. A data point verified once at the start of a multi-year mortgage journey says nothing about whether the aggregator handling it years later is still the same risk. More here.
JPMorganChase’s third-party risk chief just made the case for continuous monitoring
Dolly Singh, global head of third party oversight at JPMorganChase, argued that third-party risk management (TPRM) has not kept pace with how relationships actually work: “TPRM needs to move at machine speed.” She calls for continuous assurance to replace point-in-time review, without lowering oversight’s bar. More here.
The IDScan.net breach shows why disclosure isn’t a risk signal
A dark web marketplace sold more than 170 million identity documents traced to IDScan.net, which took nine days to confirm the breach, after reporters forced the issue. Its reach runs through a fintech integration network and loan-origination software used by lenders that never evaluated IDScan.net directly; they inherited the relationship through a platform they did choose. More here.
ChatGPT for Financial Services shows why one AI provider can mean a dozen you never vetted
OpenAI’s ChatGPT for Financial Services bundles built-in datasets, shared sign-in integrations, and a connector ecosystem exceeding 50 integrations behind one interface. A bank licensing it is not onboarding one vendor: it is inheriting a dozen-plus data providers it never reviewed, having only reviewed OpenAI – an architecture likely to spread across Open Finance chains. More here.
Six banks agree on AI agent liability – now we need proof
Six banks, including Bank of America and NatWest Group, published principles stating AI agent liability should sit where the error was introduced, not with whoever the customer was dealing with. The gap: a single transaction can cross five or six parties in seconds, and separate audit trails kept in different formats are not the same as one shared, verifiable record. More here.
New federal guidance treats API data-sharing as its own risk category
The Office of the Comptroller of the Currency (OCC), the Federal Reserve, the Federal Deposit Insurance Corporation (FDIC), and the National Credit Union Administration (NCUA) proposed guidance letting banks manage Application Programming Interface (API) data-sharing through cybersecurity controls rather than full vendor review, where access does not touch critical data. Comments are open through 16 November 2026 – the moment to establish that data-sharing and vendor risk aren’t the same thing. More here.
Amazon vs. Muse is the Open Finance vs screen-scraping fight, round two
Amazon began blocking Meta’s Muse AI shopping agent for holding customer credentials without permission, while Shopify opened its stores to the same agent – the screen-scraping fight Open Banking had, where accreditation says who’s allowed in, not whether they’re still safe. More here.
Louise Beaumont is head of marketing, communications and design at Invela
Invela is the infrastructure layer that makes Open Finance trustworthy – accrediting who’s in the network, monitoring risk in real time, and ensuring liability lands in the right place. Open Finance, covered.
Invela is an Event Partner of Open Banking Expo UK & Europe 2026. Find out more about partnering, attending and speaking here.